AI Summarized Hacker News
Front-page articles summarized hourly.
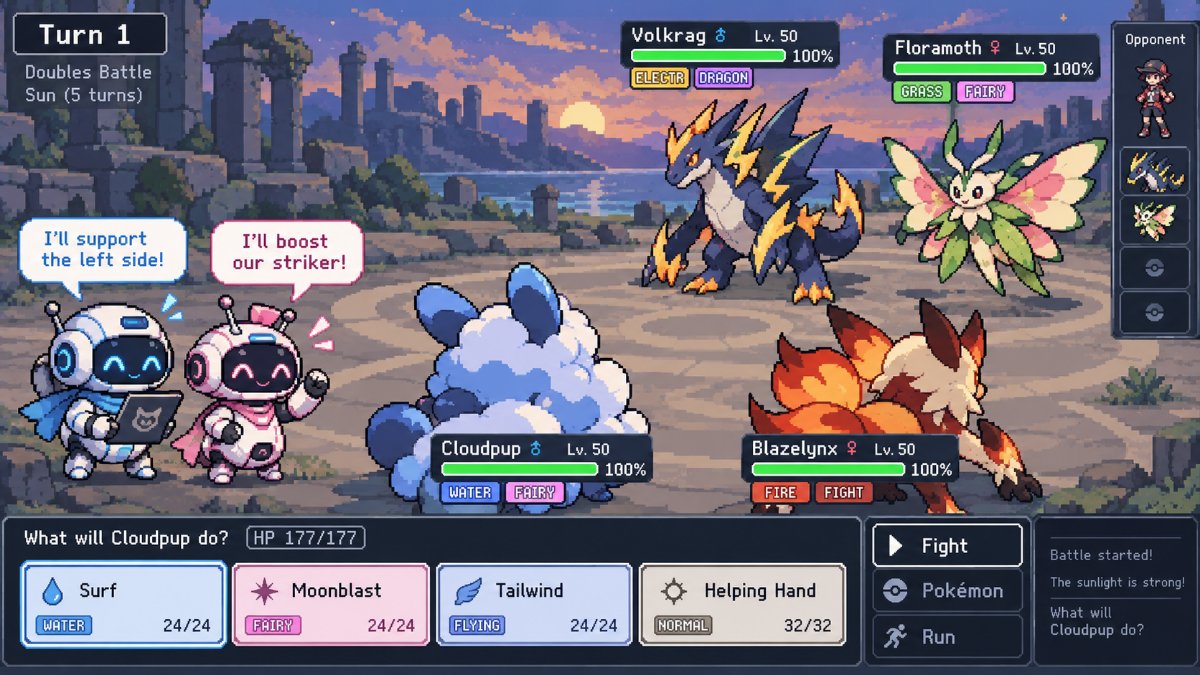
Oliver Grabner builds a Pokémon Showdown 2v2 multi-agent LLM coordination environment to study how teammates coordinate and communicate. Each turn an agent reads a battle summary, selects a move, and may message its partner. Four talk modes are evaluated: free talk, one message each, no talk, and one model controlling both Pokémon. Against a max-damage bot, free talk achieves 64% win rate, beating no-talk (42%) and one-message (52%), while one-model control is 54%. Talking increases token usage (978k vs 259k). Stronger opponents narrow gaps. Future work: separate talking from seeing moves, leaderboard benchmarks, and RL to foster collaboration.
HN Comments
A Notre Dame–backed survey of 557 Americans finds age and religiosity shape moral self-perception and self-reflection. Young adults (under 35) are most likely to feel far from the person they ought to be (38%), while 55+ respondents largely feel close or already there (about half). Older people report more daily attempts to improve character but reflect on actions less. Religiously active people reflect more than non-religious; among the young this gap is largest. Among older non-religious respondents, moral confidence dominates over reflection, suggesting greater contentment. Overall: self-improvement appears to be a younger phenomenon.
HN Comments
Bloffy is a blogging platform that lets you own and customize your blog using Markdown, HTML, CSS, and JavaScript. It emphasizes performance and privacy: pages designed for 100 on PageSpeed Insights across Web Vitals, SEO, and accessibility, with no cookies or IP logging. Features include a split editor with live preview, custom domains, CSS-driven theming, multi-language publishing with per-language URLs and JSON-LD, IndexNow support, workspace-based blogs with roles, translations management, and translation-alignment. The author invites user feedback via Discord.
HN Comments
At RustConf 2026, Tyler Mandry outlined 'Beyond the &' to align user-defined smart pointers with Rust's borrow checker by exposing the compiler's 'place' concept. The plan: create a handle type for each smart pointer and traits (BorrowPlace, WritePlace, ReadPlace, ProjectPlace) that describe how to read, write, and project from a place. This would let libraries implement pointer-like behavior as if they were built-in references, e.g., making MutexGuard-compatible accesses in shared contexts. A prototype is discussed; syntax options include BorrowPlace implemented with an @ or similar. Next steps: implement errors/diagnostics and gather community input; stabilization pending.
HN Comments

Airbnb updated its house rules to bar hosts from requiring guests to perform chores that require significant effort or would typically be done by a cleaner, for bookings made on or after Nov 20. Allowed tasks include putting used dishes in the sink, gathering towels, sorting trash and recycling into indoor bins, and turning off amenities when leaving; guests aren’t required to wash dishes, strip beds, or haul garbage off-site. A new "rules and requests" section highlights hosts’ requests, with an animal-proof trash disposal exception in bear country. Some hosts push back, and guests can avoid overly strict listings.
HN Comments
FoxIO reports QPACK amplification attacks on HTTP/3 that let a remote, unauthenticated client force a server to allocate far more memory than the compressed HEADERS on the wire. By abusing decoded-header size budgets (and missing 32-byte field overhead), a small HEADERS frame can expand to hundreds of thousands of headers, potentially exhausting memory or crashing. Seven of ten tested implementations were vulnerable; several have been fixed (quic-go, quiche, lsquic, h3, etc.), while others remain vulnerable or partially fixed. The fix is enforcing a cumulative decoded-header budget during decoding and avoiding preallocation based on compressed size.
HN Comments
The server is temporarily unavailable due to maintenance or capacity problems; please try again later.
HN Comments

PR #4441 proposes combining query thinning with fresh helper retiming for CrocSwap/integer-mult-bounds, applying the helper retiming to all 19 native calls of #4440's p17 query-thinned controller. The author-checked construction sets conditional kappa to κ = 0.00300105 (+4.105e-5 over #4440) and yields T(n) = O(n (log n)^(1 − κ)). It retains major components, notes performance/CI metrics, and credits 1337isnot1337 with OpenAI Codex assistance; review is awaited.
HN Comments
An analysis argues there is no straightforward exploit for the current PHP vulnerability. Despite widespread PoCs, most fail on a vanilla PHP setup; reliable exploitation is harder than the hype suggests. The piece critiques AI-generated claims, noting many PoCs rely on local-file-inclusion and lab conditions. While real and notable, the bug isn’t a Log4j-style catastrophe and isn’t easily weaponizable in the wild.
HN Comments

Adds a new --emudhra option to sign TLS certificates using a compromised eMudhra intermediate CA key. Introduces EMUDHRA_CHAIN_PEM, loads the EMUDHRA chain when enabled, and updates TLS config, cert store, and CLI options accordingly. Tests and UI state are extended to cover emudhra, and certifi is updated to remove eMudhra CAs from binaries.
HN Comments
Two critical PHP remote-code-execution vulnerabilities (CVE-2026-109618/109619) allow unauthenticated code execution via crafted requests. Affected PHP versions: 8.5.0–8.5.11; 8.4.0–8.4.26; 8.3.0–8.3.35; 8.2.0–8.2.34. Fixed in: 8.5.12; 8.4.27; 8.3.36; 8.2.35. End-of-life 5.4–8.1 have no upstream fix. Mitigation requires upgrading to patched releases; interim WAF rules exist. AWS services (WorkMail, Elastic Beanstalk, Amazon Linux, Lightsail) patches targeted for 2026-10-21–22; upgrade promptly.
HN Comments

CleanFrame is a starter project for a personal home screen on Samsung The Frame (Tizen), intended to be forked and adapted. It offers a browser-based preview and a set of setup scripts to run locally (Node.js 22+, Python 3.10+), then view at localhost:4795/home. You can customize layout (List/Dock), background, typography, clock, and reorder installed apps, with 15 wallpapers and local preference saving. The repo provides detailed adaptation guidance, a coding-agent workflow (AGENTS.md/docs), and TV-signing steps for public builds. MIT-licensed; hardware-specific and not guaranteed portable; contributions welcome.
HN Comments
Oracle Security Alert CVE-2026-91403 patches a remote, unauthenticated vulnerability affecting Oracle Java SE and GraalVM components. Affected products/versions: Java SE 8u511, 8u511-perf, 11.0.33, 17.0.21, 21.0.13, 25.0.5, 27.0.1; GraalVM for JDK 17.0.21, 21.0.13; GraalVM Enterprise Edition 21.3.20. Patches are released under the Security Alert program for Premier or Extended Support; customers should upgrade to supported versions. CVSS v3.1 base score 9.1; remote exploitation via networks (JSSE). Exploitation can affect Java deployments loading untrusted code; sandboxed Java Web Start applications or sandboxed applets. No credits reported.
HN Comments
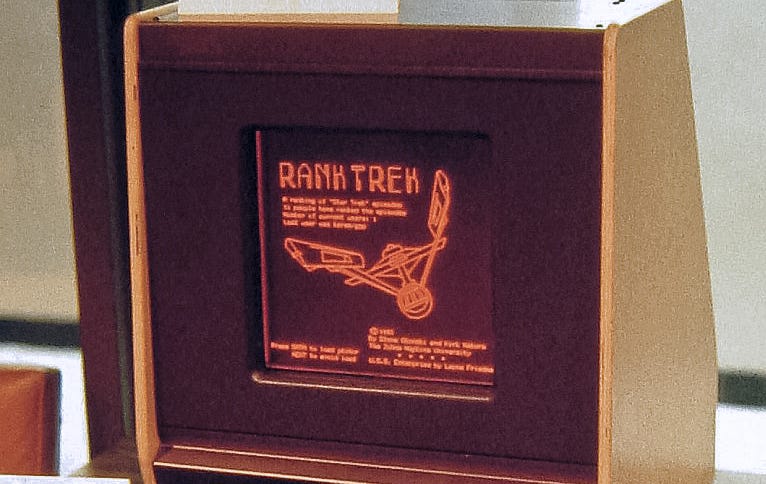
Brian Potter traces the plasma display’s rise from PLATO’s 1960s need for memory-efficient screens. Donald Bitzer’s team developed a plasma cell, overcame early issues, and Owens-Illinois commercialized panels (1968 128x128; 1971 Digivue). Plasma offered thin, rugged displays but suffered high power use and cost, lagging CRTs for many uses. Laptops saw early monochrome plasma; by the 1990s LCDs overtook color and large screens. Plasma lingered in niches until manufacturing declined in the late 2010s, effectively ending the technology.
HN Comments

An issue requests an urgent PHP security patch for Amazon Linux 2023 to fix CVE-2026-109618 and CVE-2026-109619 (CRITICAL, CVSS 9.2). The discussion cites PHP advisories around 2026-10-20/21 and says AWS/Amazon Linux will incorporate the fix into AL2023, with Elastic Beanstalk and Lightsail updates; ETA is unclear. Community members propose workarounds (building PHP SRPMs and patching) while updates rollout; EB platform 4.13.13 includes newer PHP for some versions, with targeted updates around 2026-10-22.
HN Comments

Railway reports an intrusion where an unauthorized party accessed encrypted customer environment variables and decrypted some contents, potentially exposing secrets such as API keys and registry credentials. The attack appears linked to broader campaigns targeting AI-inference providers. Upstream keys have been revoked. Even if impact seems limited, all users should rotate environment variables and private registry credentials and review logs. All deployments are paused until builds resume; Railway will contact affected customers by email and provide updates at status.railway.com as the incident scope narrows.
HN Comments
Anthropic introduced Claude Duet, a proactive agent that partners with Claude for professionals and small businesses. In a US-only research preview for Pro and Max, it runs on iOS/Android and claude.ai, shares memory from your Claude account, and works in a separate browser VM so your device can rest. It delivers a morning brief, runs tasks in the background, and checks with you before acting. It can handle admin tasks, dashboards, forecasts, and more using 6,000+ connectors (Gmail, Slack, QuickBooks, Stripe, Docusign, HubSpot, Canva, Shopify, etc.). Safety safeguards protect sensitive data; access via waitlist.
HN Comments
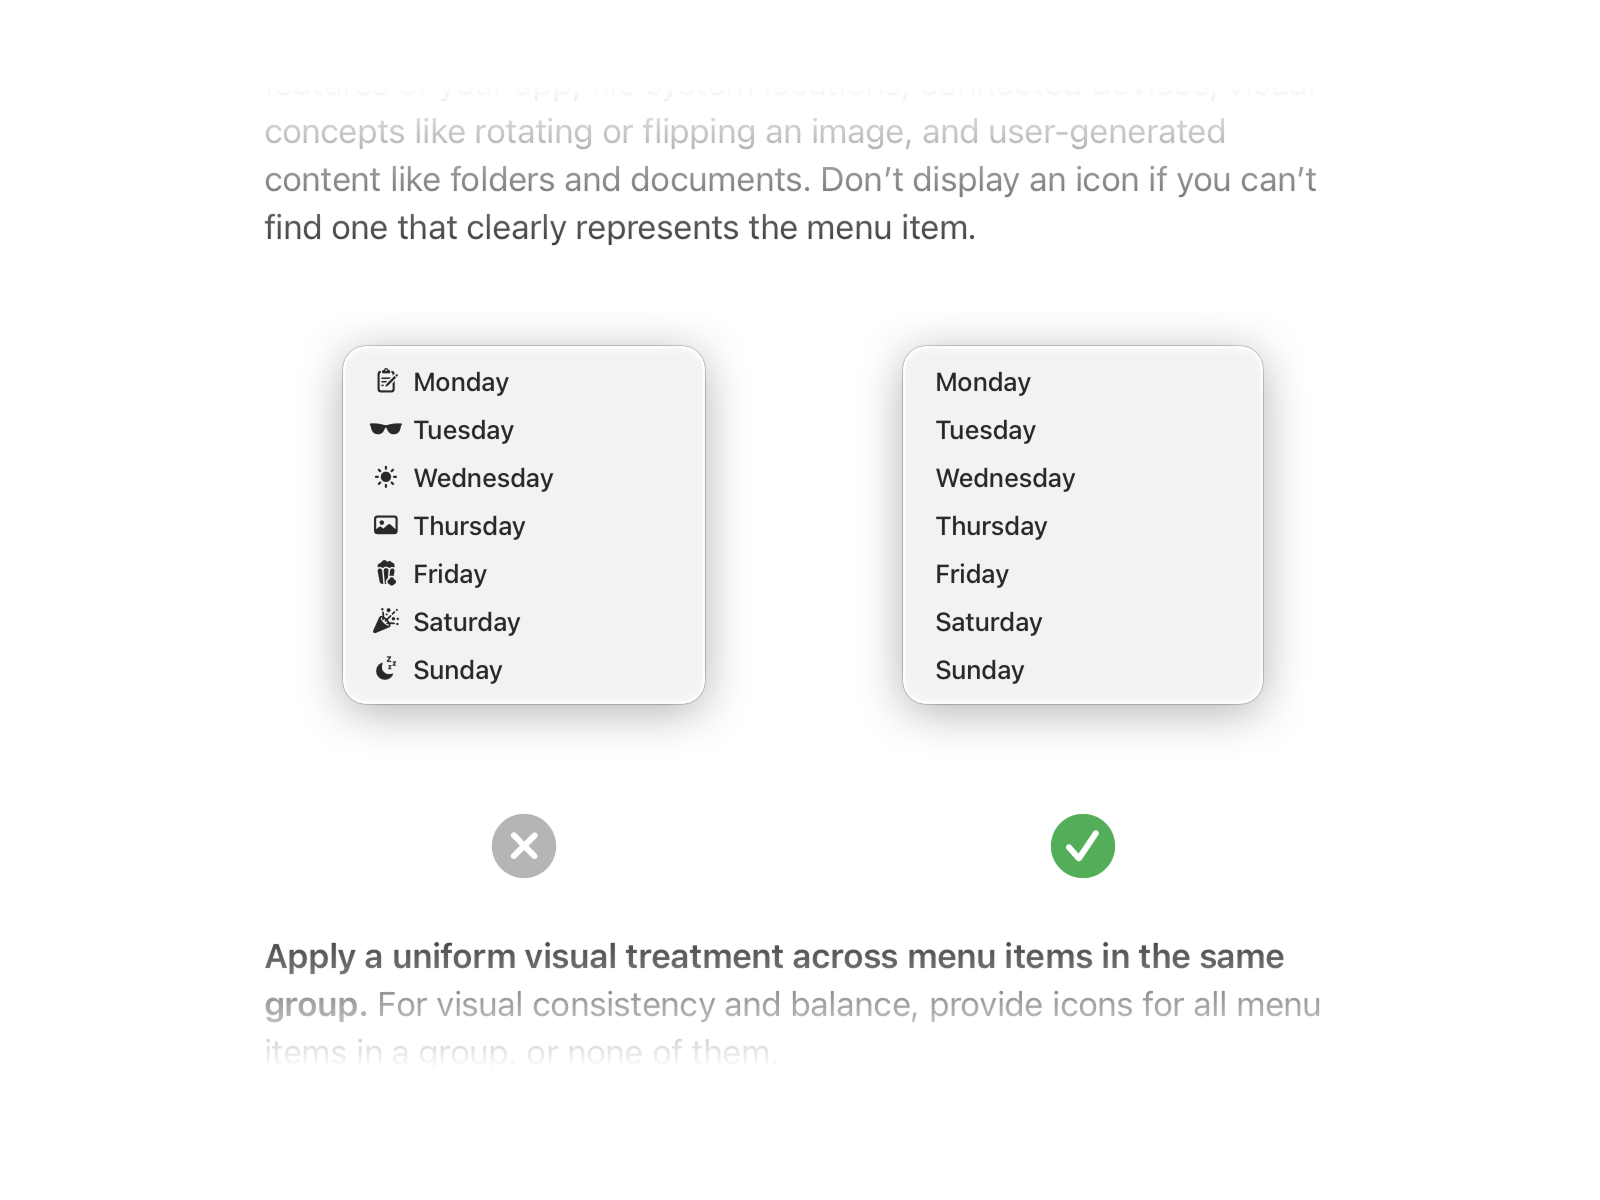
Jim Nielsen notes that macOS Tahoe shipped with icons in every menu item but Golden Gate removed them, a shift John Gruber covered and Apple’s Human Interface Guidelines now cite Tahoe as a what-not-to-do example. He argues the stronger point is Apple’s own reversal—They tried icons in all menus, shipped it, stayed with it a year, then publicly changed guidance—as proof of learning by doing.
HN Comments
Could not summarize article.
HN Comments
Could not summarize article.
HN Comments
Made by Johno Whitaker using FastHTML